



Blog
20
min read
Best AI Security Frameworks for AI Agents in 2026: NIST AI RMF, OWASP, MITRE ATLAS, ISO 42001 and SAIL Compared

20
min read
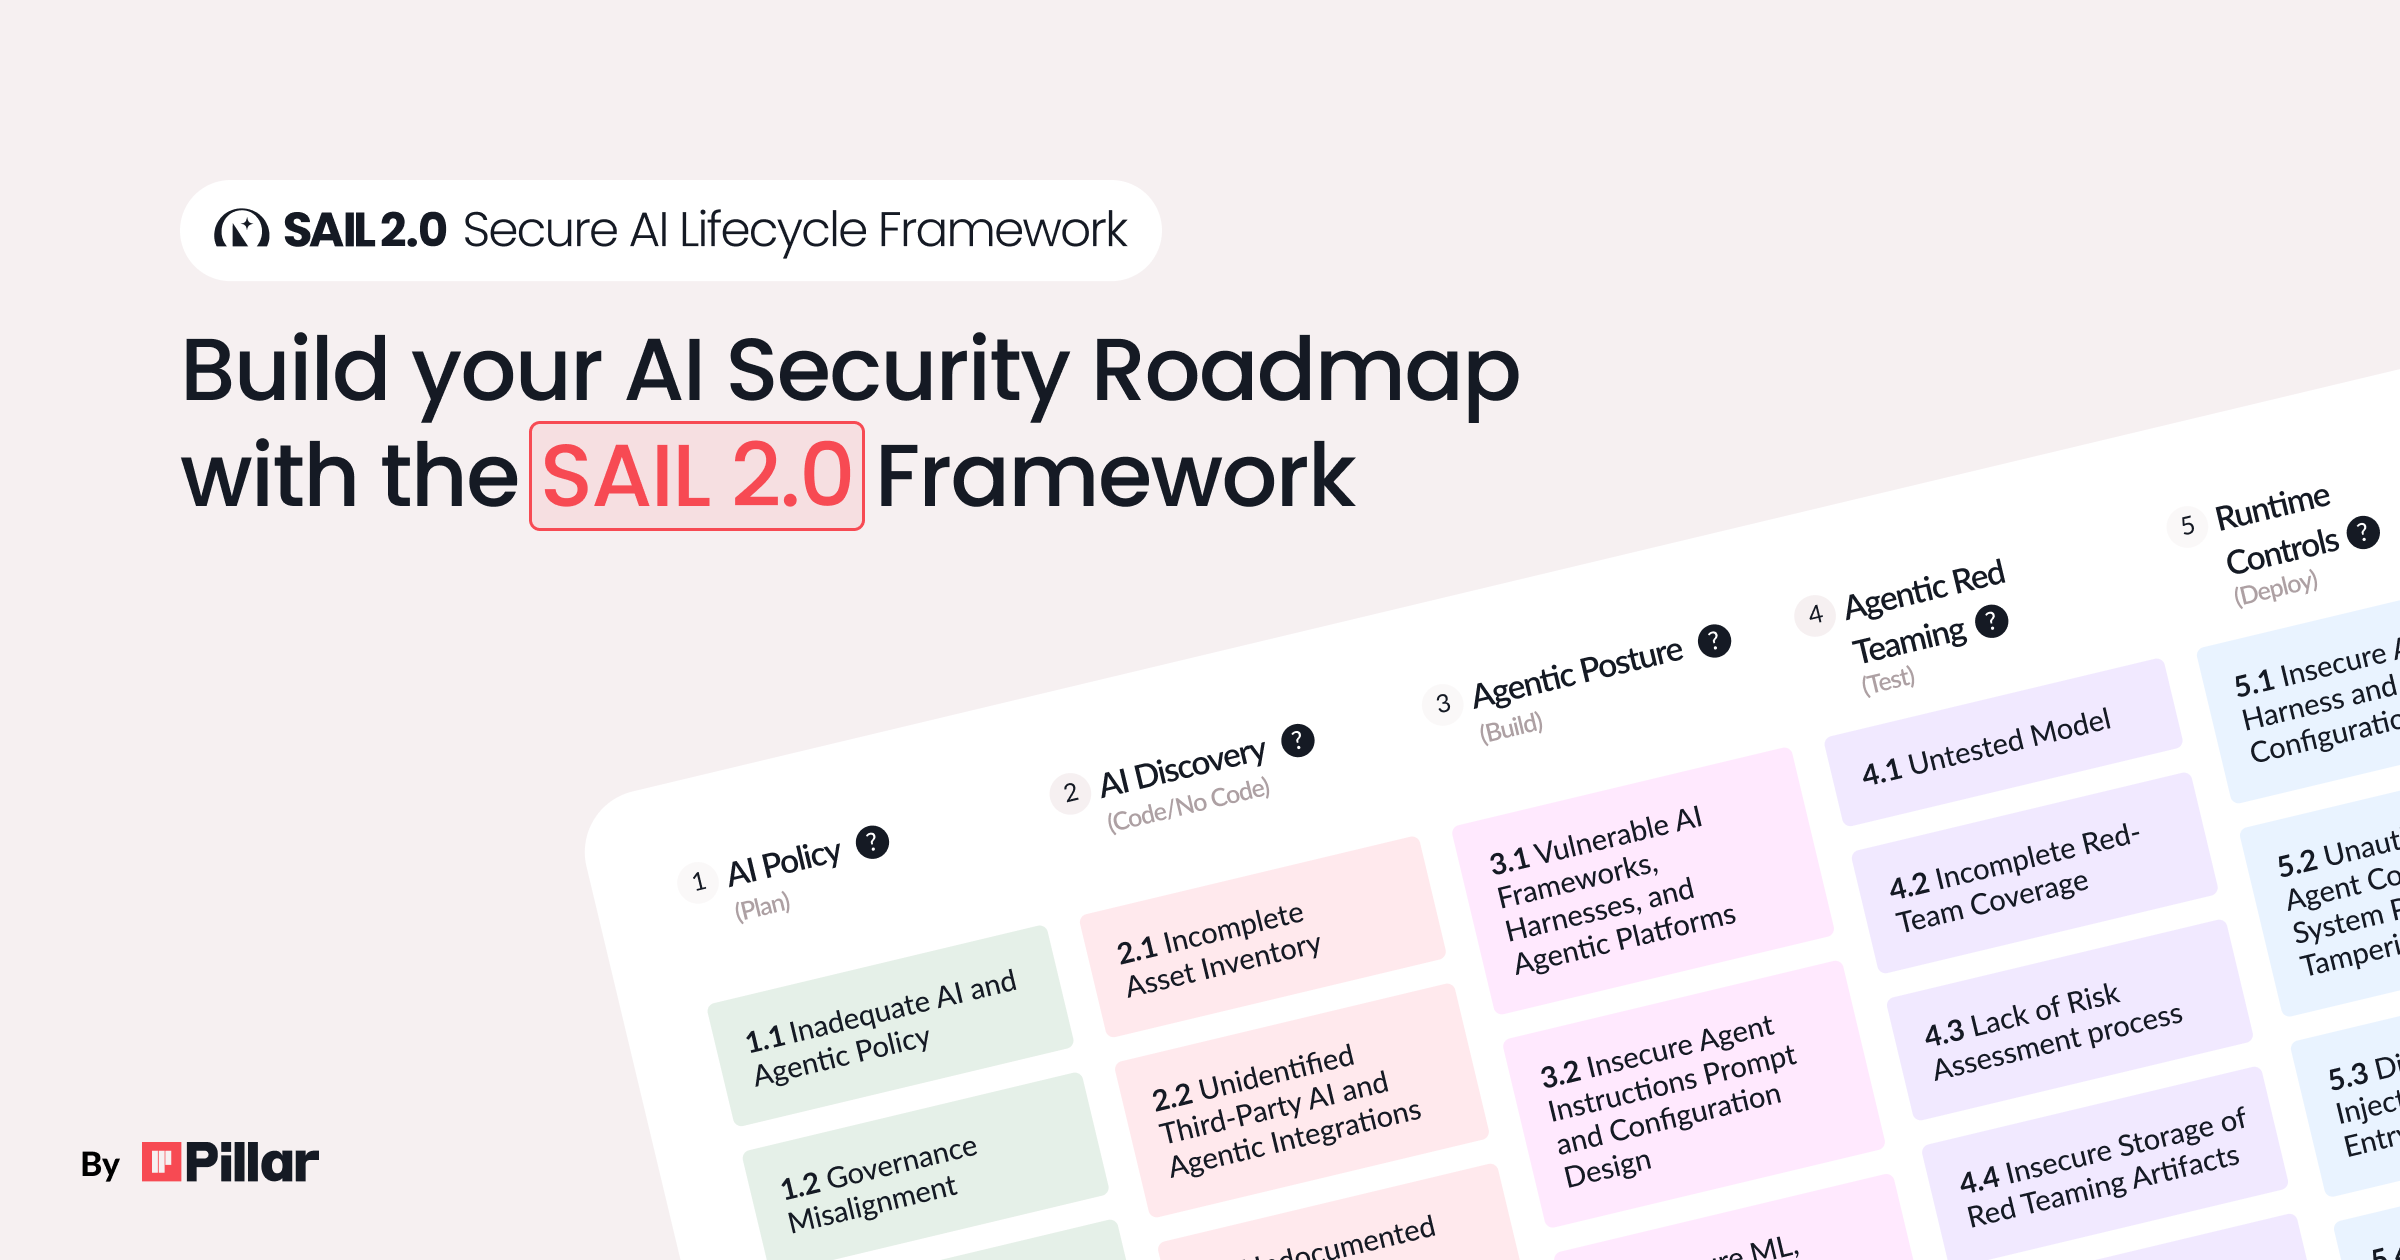
No single framework secures AI agents on its own. Enterprises in 2026 combine several: a governance framework (NIST AI RMF or ISO/IEC 42001), threat catalogs (the OWASP Top 10 for Agentic Applications and for LLM Applications, MITRE ATLAS), architecture guidance (Google SAIF, CSA MAESTRO), a control catalog for audit (CSA AI Controls Matrix, AIUC-1), and a lifecycle framework that turns all of them into a program. SAIL 2.0 is that lifecycle framework for AI agents: 7 phases and 91 agent risks, each mapped to ISO 42001, OWASP, the EU AI Act, DASF and AIUC-1.
Our recommendation: anchor governance in NIST AI RMF, or ISO/IEC 42001 if you need a certificate. Use the OWASP Agentic Top 10 and MITRE ATLAS as your threat references. Run the program with SAIL 2.0, which turns those standards into a phase-by-phase plan for AI agents and maps every risk back to them.
Framework versions and dates are as of October 7, 2026, and come from each publisher's own documents. Pillar Security publishes SAIL. We compare it on the same six questions as every other framework below, and we link each framework to its publisher so you can check our reading.
Key takeaways
- Governance frameworks (NIST AI RMF, ISO/IEC 42001) tell you who owns AI risk. They were written before AI agents and say little about tools, MCP servers, agent identity or coding agents on laptops.
- Threat catalogs (OWASP Agentic Top 10, OWASP LLM Top 10, MITRE ATLAS) tell you what can go wrong. They don't sequence the work.
- SAIL 2.0 tells you what to do, in what order, for every agent: from policy and discovery through red teaming, runtime controls, sandboxing and decommissioning, across code pipelines, cloud agents and endpoint agents.
- For an audit or certification, use ISO/IEC 42001, CSA's AI Controls Matrix (STAR for AI) or AIUC-1. SAIL's per-risk mappings show which of their controls each agent risk touches.
- Much of what ranks for this topic is out of date. In 2026 OWASP published a new LLM Top 10 edition, MITRE ATLAS moved to monthly releases, DASF reached v3.0 with agentic risks, CSA released AICM v1.1, and the EU moved the AI Act's Annex III high-risk deadline to December 2, 2027.
What is an AI security framework?
An AI security framework is a published structure for identifying, prioritizing and controlling the security risks of AI systems, such as models, applications and agents. Frameworks differ in what they give you. Some define governance outcomes, some list threats, some prescribe controls you can be audited against, and some lay out a lifecycle of activities.
That difference is why "which framework is best" has no one-name answer. Most mature AI security programs use one framework of each type:
| Type | Question it answers | Examples |
|---|---|---|
| Governance and risk management | Who owns AI risk, and how is it managed? | NIST AI RMF, ISO/IEC 42001 |
| Threat taxonomy | What can go wrong? | OWASP Agentic Top 10, OWASP LLM Top 10, MITRE ATLAS |
| Architecture and threat modeling | Where in the stack should controls live? | Google SAIF, CSA MAESTRO |
| Control catalog and assurance | How do we prove it to auditors and customers? | CSA AI Controls Matrix, AIUC-1, ISO/IEC 42001 certification |
| Platform-specific | How do we secure AI on this data platform? | Databricks DASF |
| Lifecycle operating framework | What do we do, in what order, for every agent? | SAIL 2.0 |
| Regulation | What does the law require? | EU AI Act |
Why do AI agents need more than an LLM security framework?
Because an agent acts. An LLM application answers questions. An agent calls tools, connects to MCP servers, holds credentials, keeps memory, runs on a developer's laptop or inside a SaaS platform, and hands work to other agents. Each of those adds an attack surface that the first generation of AI frameworks did not name.
The 2026 framework releases follow that shift. OWASP gave agents their own Top 10 (ASI01 to ASI10) and now hands agent risks over to it from the LLM list. MITRE ATLAS added agent techniques such as discovering an agent's runtime capabilities. DASF v3.0 added an agentic AI component. When you choose frameworks, check that at least one of them covers:
- Tool and MCP server permissions
- Agent identity and delegated authority
- Memory and context poisoning
- Coding agents and other agents running on endpoints
- Multi-agent handoffs
- Decommissioning agents and revoking their access
The best AI security frameworks for AI agents at a glance
Ordered by how directly each one tells an enterprise what to do about AI agents. Versions are as of October 7, 2026.
| Framework | Publisher | Latest version | Type | Best for |
|---|---|---|---|---|
| 1. SAIL 2.0 (Secure AI Lifecycle) | Pillar Security, with industry contributors | 2.0, July 2026 | Lifecycle operating framework | Running an AI agent security program end to end, mapped to the major standards |
| 2. OWASP Top 10 for Agentic Applications | OWASP GenAI Security Project | 2026 edition, December 2025 | Threat taxonomy | A shared vocabulary for agent risks (ASI01 to ASI10) |
| 3. NIST AI Risk Management Framework | NIST | AI RMF 1.0 (January 2023) plus the Generative AI Profile, NIST AI 600-1 (July 2024) | Governance and risk management | Board-level AI risk governance, especially in the US |
| 4. MITRE ATLAS | MITRE | v2026.09, September 2026 | Adversary tactics and techniques | Threat modeling, red team planning and detection engineering |
| 5. ISO/IEC 42001 | ISO/IEC JTC 1/SC 42 | 42001:2023 | Certifiable management system | An auditable, certifiable AI management system |
| 6. OWASP Top 10 for LLM Applications | OWASP GenAI Security Project | 2026 edition, August 2026 | Threat taxonomy | Securing LLM-powered applications and the model as a component |
| 7. CSA AI Controls Matrix (AICM) | Cloud Security Alliance | v1.1, July 2026 | Control catalog | Vendor and cloud assurance, and STAR for AI |
| 8. Google Secure AI Framework (SAIF) | SAIF 2.0, October 2025 | Principles and risk map | Security architecture principles, especially on Google Cloud | |
| 9. CSA MAESTRO | Cloud Security Alliance | v1, February 2025 (v2 in review) | Layered threat model for agents | Threat modeling multi-agent systems layer by layer |
| 10. AIUC-1 | AIUC-1 Consortium | Quarterly releases; latest July 2026 | Certification standard for AI agents | Certifying an AI agent product for enterprise buyers |
| 11. Databricks AI Security Framework (DASF) | Databricks | v3.0, March 2026 | Platform risk and control catalog | AI and agent workloads on a data platform such as Databricks |
Pillar Security publishes SAIL. On smaller screens, scroll the table sideways.
The EU AI Act is a regulation, not a framework. Several of the frameworks above map to it, and it has its own section below.
How we compared the AI security frameworks
We asked six questions of each framework, using its publisher's own documents.
- Agents: does it name agent-specific risks such as tools, MCP servers, agent identity, memory and endpoint agents?
- Prescriptive: does it say what to do, or only what can go wrong?
- Lifecycle: does it cover the whole life of an AI system, from policy to decommissioning?
- Mapped: does it map to other standards, so one piece of work satisfies several?
- Certifiable: can an organization or product be audited or certified against it?
- Current: has it been updated in 2026?
| Framework | Agents | Prescriptive | Lifecycle | Mapped | Certifiable | Current (2026) |
|---|---|---|---|---|---|---|
| SAIL 2.0 | Yes | Yes: mitigations for each of its 91 risks | Yes: 7 phases, including retirement | Yes: each risk mapped to 6 standards | No | Yes |
| OWASP Agentic Top 10 | Yes | Partial: mitigations per risk | No | Partial | No | Yes |
| NIST AI RMF | No: agent guidance is still in development at NIST | Partial: outcomes plus suggested actions | Yes | Partial | No | No: a revision is under way |
| MITRE ATLAS | Yes | Partial: 40 mitigations | No: it follows the attack, not the system | Partial: modeled on ATT&CK | No | Yes: monthly |
| ISO/IEC 42001 | No | Partial: Annex A controls | Yes | Partial | Yes | No |
| OWASP LLM Top 10 | Partial: agent risks hand off to the Agentic Top 10 | Partial | No | Yes: crosswalk appendix | No | Yes |
| CSA AICM | Partial | Yes: 247 controls | Partial | Yes | Yes: STAR for AI | Yes |
| Google SAIF | Yes: agent risk map in SAIF 2.0 | Partial: principles | Partial | Partial | No | No: last major update October 2025 |
| CSA MAESTRO | Yes | Partial: a threat model | No | Partial | No | Partial: v2 in review |
| AIUC-1 | Yes | Yes | Partial | Partial | Yes | Yes: quarterly |
| DASF v3.0 | Yes: agentic AI component | Yes: 73 controls | Partial | Partial | No | Yes |
Ratings are our reading of each publisher's documents as of October 7, 2026. On smaller screens, scroll the table sideways.
The 11 AI security frameworks compared
1. SAIL 2.0 (Secure AI Lifecycle), by Pillar Security
Best for: security and AI platform teams that need one operating plan for AI agents across code pipelines, cloud platforms and developer endpoints, mapped to the standards their auditors and regulators use.
What it is. SAIL is a process-oriented framework for securing AI systems and AI agents across their lifecycle. Pillar first published it in July 2025, written with security leaders from companies including Google Cloud, Microsoft, Salesforce, ServiceNow, AT&T, SAP, Nestlé and Corning. SAIL 2.0 followed in July 2026, rebuilt for agents and with contributors including JPMorganChase. The framework has been downloaded more than 50,000 times, and in its report “Coolest Vendor Innovations in AI Software Security 2026”, Gartner® highlighted the SAIL Framework.
How it's structured. SAIL has three parts.
- Seven lifecycle phases, which follow the software lifecycle so security, engineering and governance teams can work from one plan.
- Three zones, which describe where agent risk lives. Zone 1 is AI assets in code and pipelines: models, prompts, MCP definitions and agent configs in source control, CI and registries. Zone 2 is cloud agents running inside managed platforms and SaaS tools. Zone 3 is endpoint agents, such as coding assistants and browser agents running on employee machines under the user's identity.
- A 91-risk catalog. Each risk has a stable ID (SAIL 1.1 to SAIL 7.7), a description, mitigations and mappings. The catalog is built on 29 agentic components in six layers, from the agent harness and MCP servers to agent identity and memory.
| Phase | What it secures | Risks | Example risk |
|---|---|---|---|
| 1. AI Policy (Plan) | Policy, risk tolerance, threat modeling, autonomy tiers, agent identity policy | 13 | SAIL 1.13 No Agentic Identity Policy Defined |
| 2. AI Discovery (Code/No Code) | Inventory of models, agents, integrations, agent identities and endpoint agents | 8 | SAIL 2.8 Unvetted Local / Endpoint Agents |
| 3. Agentic Posture Management (Build) | Configuration, permissions, credentials, MCP definitions and posture drift | 18 | SAIL 3.13 Over-Scoped Agent Tool Permissions and Connectors |
| 4. Agentic Red Teaming (Test) | Adversarial testing of agents, tool chains, memory and multi-agent workflows | 11 | SAIL 4.8 Untested Tool Chain and Multi-Agent Workflows |
| 5. Runtime Controls (Deploy) | Prompt injection, tool result poisoning, data exfiltration, action-level authorization | 20 | SAIL 5.4 Indirect / Cross-Source Prompt Injection (XPIA) |
| 6. Sandbox (Operate) | Isolation, tool invocation limits, self-modification, irreversible actions | 14 | SAIL 6.11 Endpoint Agent Sandbox Bypass |
| 7. Govern (Monitor and Retire) | Logging, alerts, drift, incident response and decommissioning | 7 | SAIL 7.7 Untracked Agent Decommissioning |
How it maps to other standards. Each SAIL risk cites the controls it touches in ISO/IEC 42001, the OWASP Top 10 for Agentic Applications (2026), the OWASP Top 10 for LLM Applications (2025), the EU AI Act, Databricks DASF v3.0 and AIUC-1. A standard is left out of a row when it doesn't address that risk. For example:
| SAIL risk | OWASP Agentic | OWASP LLM (2025) | ISO/IEC 42001 | EU AI Act | AIUC-1 |
|---|---|---|---|---|---|
| 1.13 No Agentic Identity Policy Defined | ASI03 | LLM06 | A.4.5, A.4.6 | Art. 15(5) | B007, E004 |
| 2.8 Unvetted Local / Endpoint Agents | ASI04, ASI10 | LLM03 | A.3.2, A.10.3 | Art. 17 | E006, E010 |
| 3.17 Unvetted MCP Server Definitions | ASI04, ASI02 | LLM03 | A.10.3, A.4.4 | Art. 25, Art. 15(5) | E006, B006 |
| 4.8 Untested Tool Chain and Multi-Agent Workflows | ASI02, ASI07 | LLM06 | A.6.2.4 | Art. 15 | B001, D004 |
| 5.4 Indirect / Cross-Source Prompt Injection (XPIA) | ASI01, ASI06 | LLM01 | A.7.6 | Art. 15(5) | B001, B005 |
| 6.11 Endpoint Agent Sandbox Bypass | ASI05, ASI02 | LLM06 | A.4.5, A.6.2.6 | Art. 15(5) | B008, B006 |
| 7.5 Absence of AI- and Agent-Specific Incident Response Plan | ASI10, ASI08 | None | A.8.4, A.6.1.3 | Art. 73 | E001, E002 |
Source: the SAIL 2.0 risk catalog. Each risk also maps to Databricks DASF v3.0 controls.
SAIL cites the 2025 numbering of the OWASP LLM list. The 2026 edition renumbered eight of the ten entries; Excessive Agency, for example, moved from LLM06 to LLM03.
Limitations to know: SAIL is not a certification, so pair it with ISO/IEC 42001, AICM or AIUC-1 when you need an attestation. Its per-risk mappings cover ISO 42001, OWASP, the EU AI Act, DASF and AIUC-1; for NIST AI RMF, the crosswalk later in this article lines up SAIL's phases with NIST's four functions.
How to use it: read the full catalog at pillar.security/sail, or install the SAIL agent skill in Claude Code, Codex, ChatGPT or Antigravity. The skill can assess an agent against the 91 risks, draft a phased roadmap, and produce a compliance view across the mapped standards.
2. OWASP Top 10 for Agentic Applications (2026)
Best for: giving engineering, security and vendors one vocabulary for agent threats, and scoping red team tests.
What it is. The OWASP GenAI Security Project's Top 10 for Agentic Applications, published in December 2025, is the most widely cited list of agent-specific risks. It runs from ASI01 Agent Goal Hijack through ASI02 Tool Misuse and Exploitation, ASI03 Identity and Privilege Abuse, ASI04 Agentic Supply Chain Vulnerabilities, ASI05 Unexpected Code Execution, ASI06 Memory and Context Poisoning, ASI07 Insecure Inter-Agent Communication, ASI08 Cascading Failures and ASI09 Human-Agent Trust Exploitation, to ASI10 Rogue Agents. It also introduces the principle of least agency.
Limitations to know: it is a risk list, not a program. It doesn't cover discovery, inventory, governance or decommissioning, and it isn't certifiable. Every SAIL risk that involves agents cites the ASI entries it relates to.
3. NIST AI Risk Management Framework (AI RMF)
Best for: setting up AI risk governance that boards, regulators and US federal buyers recognize.
What it is. NIST's AI RMF 1.0 (January 2023) organizes AI risk management into four functions: Govern, Map, Measure and Manage. The Generative AI Profile, NIST AI 600-1 (July 2024), adapts it to generative AI. NIST has said the AI RMF is being revised. Its agent work is still at an early stage (as of October 7, 2026): the Center for AI Standards and Innovation (CAISI) ran an RFI on AI agent security in early 2026 and launched an AI Agent Standards Initiative in February 2026, and a preliminary draft Cyber AI Profile (NIST IR 8596) was published in December 2025.
Limitations to know: it is voluntary and outcome-based. It tells you to map and manage risk, not how to control an agent's tool permissions or MCP servers. Teams usually pair it with a threat catalog and an operating framework.
4. MITRE ATLAS
Best for: threat modeling, planning red team scenarios, and mapping detections to known adversary behavior.
What it is. MITRE ATLAS (Adversarial Threat Landscape for Artificial-Intelligence Systems) is a knowledge base of adversary tactics and techniques against AI systems, modeled on MITRE ATT&CK. Version 2026.09 lists 16 tactics, 120 techniques, 88 sub-techniques, 40 mitigations and 73 case studies. Since mid-2026 it has been released monthly, and recent releases added agent techniques such as discovering an agent's runtime capabilities.
Limitations to know: it describes attacks, not your program. It has no governance, inventory or policy layer.
5. ISO/IEC 42001
Best for: organizations that need a certificate to show customers or regulators. ISO 42001 work also covers a substantial part of what the EU AI Act asks for.
What it is. ISO/IEC 42001:2023 specifies an AI management system (AIMS), using the same management-system structure as ISO/IEC 27001. Annex A lists the reference control objectives. Organizations can be certified against it, and certificates are valid for three years. Related standards include ISO/IEC 42005 for AI system impact assessment (2025). ISO/IEC 27090, guidance on AI security threats, was listed as under publication (as of October 7, 2026).
Limitations to know: it is a management-system standard written in 2023. It requires you to assess and treat AI risks but doesn't list agent threats or technical controls for them. Each SAIL risk cites the ISO/IEC 42001 clauses and Annex A controls it relates to.
6. OWASP Top 10 for LLM Applications (2026 edition)
Best for: securing LLM-powered applications and the model as a component.
What it is. OWASP's Top 10 for LLM Applications is the original list of LLM application risks. The 2026 edition (August 2026) is the first to weigh incident data alongside practitioner votes, and it reordered the list: LLM01 Prompt Injection, LLM02 Sensitive Information Disclosure, LLM03 Excessive Agency, LLM04 Supply Chain, LLM05 Data and Model Poisoning, LLM06 Unbounded Consumption, LLM07 Misinformation, LLM08 Hidden Context Exposure, LLM09 Vector and Embedding Weaknesses and LLM10 Improper Output Handling. Its appendix crosswalks each entry to the Agentic Top 10, MITRE ATLAS, NIST and other standards.
Limitations to know: once a model acts as an agent, OWASP hands the risk to the Agentic Top 10. Check which edition your tools and reports cite, because most IDs changed between 2025 and 2026.
7. CSA AI Controls Matrix (AICM)
Best for: cloud and AI vendor assurance, third-party risk questionnaires and a STAR for AI attestation.
What it is. The Cloud Security Alliance's AI Controls Matrix is a vendor-neutral control catalog for AI systems. Version 1.1 (July 2026) has 247 controls across 18 domains, including a model security domain. It is the basis for CSA's STAR for AI assurance program.
Limitations to know: a control catalog this size needs a plan to prioritize it. Most teams use a lifecycle framework or threat model to decide which controls apply to which agent first.
8. Google Secure AI Framework (SAIF)
Best for: architecture principles, and teams building agents on Google Cloud.
What it is. Google's SAIF (June 2023) sets out principles for secure AI systems. SAIF 2.0 (October 2025) added an agent risk map and three principles for agents, and Google donated the risk map data to the Coalition for Secure AI (CoSAI). Google's guidance separates model controls from agent controls, the second covering goals, access boundaries and downstream risk.
Limitations to know: principles need translating into controls and an operating rhythm. SAIL and SAIF fit together: SAIF describes how a secure agent should be designed, and SAIL describes the activities that keep it secure from policy to retirement.
9. CSA MAESTRO
Best for: threat modeling a specific multi-agent system and deciding which layer a mitigation belongs in.
What it is. MAESTRO is the Cloud Security Alliance's threat modeling framework for agentic AI, published in February 2025. It splits an agent system into seven layers, from foundation models through data operations, agent frameworks, deployment, observability and compliance, to the agent ecosystem, and analyzes threats at each layer and between them. A second version was in peer review in mid-2026.
Limitations to know: it is a threat modeling method, not a control set or a program. It fits inside SAIL's Plan phase, where threat modeling for AI and agentic systems is risk 1.9.
10. AIUC-1
Best for: companies selling AI agents that need to show enterprise buyers an independent certification.
What it is. AIUC-1 is a certification standard for AI agents, maintained by the AIUC-1 Consortium. Its requirements are grouped in six domains with control IDs from A001 to F002. It has been updated quarterly since its first release in July 2025; the latest release was July 2026 (as of October 7, 2026).
Limitations to know: a certificate attests to the vendor's controls at a point in time. Buyers still need to test and monitor the agents they deploy. Each SAIL risk cites the AIUC-1 controls it relates to.
11. Databricks AI Security Framework (DASF)
Best for: teams running AI and agent workloads on Databricks or a similar lakehouse.
What it is. DASF catalogs AI risks and controls across the components of a data and AI platform. Version 3.0 (March 2026) covers 97 risks and 73 controls across 13 components, including a new agentic AI component with sub-areas for agent cores, MCP servers and MCP clients.
Limitations to know: its controls are written with the Databricks platform in mind. SAIL maps each of its risks to DASF v3.0, so platform teams can carry DASF controls into an organization-wide program.
Where does the EU AI Act fit?
The EU AI Act is law, not a framework, and frameworks are how most companies prepare for it. The Digital Omnibus amendment, Regulation (EU) 2026/1744, in force since July 27, 2026, moved the main high-risk deadlines of Regulation (EU) 2024/1689 (as of October 7, 2026):
- Prohibited practices: applied from February 2, 2025.
- General-purpose AI model obligations: applied from August 2, 2025.
- High-risk systems listed in Annex III: now apply from December 2, 2027.
- High-risk AI in products covered by Annex I: now apply from August 2, 2028.
SAIL cites EU AI Act articles for each risk where one applies, for example Article 15 on accuracy, robustness and cybersecurity, Article 14 on human oversight and Article 73 on serious incident reporting. See our analysis of what the EU AI Act deferral bought you.
How do the AI security frameworks fit together?
Use one framework per layer. A practical stack for an enterprise securing AI agents in 2026 looks like this:
- Governance: NIST AI RMF for the risk management model, or ISO/IEC 42001 if you need certification.
- Threat references: the OWASP Agentic Top 10 for agents, the OWASP LLM Top 10 for model-facing applications, and MITRE ATLAS for adversary techniques.
- Operating framework: SAIL 2.0 to sequence the work for every agent, phase by phase and zone by zone.
- Assurance: CSA AICM, AIUC-1 or ISO/IEC 42001 certification, depending on who is asking for evidence.
- Platform and architecture guidance where it applies: SAIF on Google Cloud, DASF on Databricks, MAESTRO for threat modeling complex multi-agent systems.
Because NIST AI RMF is the governance anchor for many US enterprises, here is how SAIL's phases line up with its four functions. This crosswalk is ours, not an official NIST mapping.
| SAIL phase | NIST AI RMF function | What the overlap covers |
|---|---|---|
| 1. AI Policy (Plan) | Govern, Map | Policies, risk tolerance, roles, threat modeling |
| 2. AI Discovery (Code/No Code) | Map | Inventory of AI systems, agents, integrations and their context |
| 3. Agentic Posture Management (Build) | Map, Measure | Assessing configuration, permissions and exposure |
| 4. Agentic Red Teaming (Test) | Measure | Testing and evaluating risks before and after deployment |
| 5. Runtime Controls (Deploy) | Manage | Treating risks in production |
| 6. Sandbox (Operate) | Manage | Containing agent actions and limiting impact |
| 7. Govern (Monitor and Retire) | Govern, Manage | Monitoring, incident response and decommissioning |
Which AI security framework should I use?
Start from the job you need done. Most teams combine two or three of these.
| If you need to… | Start with | Add |
|---|---|---|
| Build an AI agent security program from scratch | SAIL 2.0 | NIST AI RMF for governance language |
| Report AI risk to the board | NIST AI RMF | SAIL phases as the delivery plan |
| Get certified | ISO/IEC 42001 | SAIL's per-risk ISO mappings to find control gaps |
| Prepare for the EU AI Act | ISO/IEC 42001 | SAIL's per-risk article mappings |
| Secure coding agents on developer laptops | SAIL Zone 3 risks (2.8, 4.11, 6.11) | OWASP Agentic Top 10 (ASI02, ASI04, ASI05) |
| Plan an AI red team engagement | MITRE ATLAS and the OWASP Agentic Top 10 | SAIL phase 4 for coverage gaps such as multi-agent and endpoint testing |
| Answer vendor and customer questionnaires | CSA AICM | AIUC-1 if you sell an AI agent |
| Threat model a multi-agent system | CSA MAESTRO | MITRE ATLAS techniques |
| Secure AI on Databricks or Google Cloud | DASF or SAIF | SAIL to cover agents outside that platform |
How do I put SAIL into practice?
Start with visibility, then add controls in lifecycle order.
- Write the policy (phase 1). Define acceptable use, risk tolerance, an autonomy tier for each agent (SAIL 1.11), a vetting path for MCP servers and tools (1.10), and an agent identity policy (1.13).
- Find every agent (phase 2). Inventory models, agents, MCP servers, third-party AI integrations and agent identities in all three zones, including coding agents on endpoints (2.8).
- Fix posture before you test (phase 3). Remove over-scoped tool permissions (3.13), exposed credentials (3.9, 3.12) and unreviewed MCP definitions (3.17), and watch for drift (3.18).
- Red team agents, not only models (phase 4). Cover tool chains, multi-agent workflows, memory and endpoint agent behavior (4.8 to 4.11).
- Enforce at runtime and contain (phases 5 and 6). Add guardrails for direct and indirect prompt injection (5.3, 5.4), action-level authorization (5.13) and sandboxing (6.1, 6.11).
- Monitor and retire (phase 7). Log agent interactions (7.1), prepare an incident response plan for agent incidents (7.5), and revoke access when an agent is decommissioned (7.7).
To check an existing agent, run the SAIL skill's assessment command in your coding agent. It walks through the 91 risks and returns findings with their standards mappings.
How Pillar helps. Pillar's platform discovers AI assets and agents across code, cloud and endpoints, tests them with continuous agentic red teaming, and enforces runtime guardrails. Its discovery, posture and red-teaming findings carry SAIL risk IDs, so the results map straight to the framework and the standards behind it. See Agentic Endpoint and Runtime Guardrails.
What changed in AI security frameworks in 2026?
- February 2026: NIST's CAISI launched the AI Agent Standards Initiative.
- March 2026: Databricks released DASF v3.0, adding agentic AI risks and controls.
- Mid-2026: MITRE ATLAS moved to date-based monthly releases and added agent techniques. v2026.09 has 120 techniques.
- July 2026: Pillar released SAIL 2.0, with three zones, a 91-risk agent catalog and per-risk mappings to six standards. CSA released AICM v1.1 with 247 controls. AIUC-1 shipped its quarterly update. The EU's Digital Omnibus entered into force, moving Annex III high-risk obligations to December 2, 2027.
- August 2026: OWASP published the 2026 edition of the Top 10 for LLM Applications, which moved Excessive Agency to LLM03 and renamed System Prompt Leakage to Hidden Context Exposure.
- Pending (as of October 7, 2026): ISO/IEC 27090 on AI security, a revision of NIST AI RMF, NIST control overlays for AI agents (COSAiS), and version 2 of CSA MAESTRO.
Next steps
- Read the SAIL 2.0 framework and its 91-risk catalog.
- Install the SAIL skill and assess one of your agents.
- See SAIL applied to a real incident: the Amazon Q extension compromise.
- Compare tools for each phase: AI red teaming providers, AI coding agent security tools and AI gateway guardrails.
FAQs
What is the best AI security framework for AI agents?
Use a combination. NIST AI RMF or ISO/IEC 42001 for governance, the OWASP Agentic Top 10 and MITRE ATLAS for threats, and SAIL 2.0 as the operating framework. SAIL is written for agents: 7 lifecycle phases, 3 zones and 91 risks, each mapped to ISO 42001, OWASP, the EU AI Act, DASF and AIUC-1.
What is the SAIL framework?
SAIL (Secure AI Lifecycle) is a free, process-oriented framework for securing AI systems and agents, published by Pillar Security with industry contributors. Version 2.0 (July 2026) organizes 91 agent risks into seven phases, from policy and discovery to runtime controls, sandboxing and decommissioning, and maps each risk to six standards.
How is SAIL different from NIST AI RMF?
NIST AI RMF defines governance outcomes in four functions (Govern, Map, Measure, Manage) and doesn't address agent-specific risks in detail. SAIL is operational: it lists the agent risks and mitigations for each lifecycle phase. Many teams use NIST AI RMF as the governance model and SAIL as the delivery plan.
How is SAIL different from the OWASP Top 10 for Agentic Applications?
The OWASP list names the ten most important agent risk categories. SAIL is a lifecycle program with 91 specific risks and mitigations, and it cites the OWASP ASI entries each risk relates to. Use OWASP for the vocabulary and SAIL for the plan.
Is NIST AI RMF enough to secure AI agents?
Not on its own. It was published in January 2023, and NIST's agent-specific work, including the CAISI AI Agent Standards Initiative and control overlays for agents, was still in development as of October 2026. Pair it with an agent threat catalog and an operating framework.
Which AI security frameworks can you be certified against?
ISO/IEC 42001 (an AI management system certificate), CSA's STAR for AI, which is based on the AI Controls Matrix, and AIUC-1 for AI agent products. NIST AI RMF, the OWASP lists, MITRE ATLAS, SAIF, MAESTRO and SAIL are not certifications.
Does MITRE ATLAS cover AI agents?
Yes. ATLAS has added agent techniques through 2026, such as discovering an agent's runtime capabilities. Version 2026.09 lists 16 tactics, 120 techniques and 40 mitigations. It describes attacker behavior, so pair it with a framework that tells you which controls to run.
What is the difference between Google SAIF and SAIL?
SAIF is a set of security principles and a risk map for AI systems, extended to agents in SAIF 2.0. SAIL is a lifecycle framework that lists 91 agent risks and the activities to address them in each phase. SAIF guides how a secure agent is designed; SAIL guides how it is secured from policy to retirement.
How do AI security frameworks map to the EU AI Act?
ISO/IEC 42001 covers much of the Act's management-system expectations. SAIL cites the relevant article for each risk where one applies, such as Article 14 (human oversight), Article 15 (robustness and cybersecurity) and Article 73 (incident reporting). Annex III high-risk obligations now apply from December 2, 2027.
Is SAIL free?
Yes. The SAIL framework and its 91-risk catalog are free to read at pillar.security/sail, and the SAIL agent skill is on GitHub under a Creative Commons non-commercial licence that allows use inside your organization.
Subscribe and get the latest security updates

Back to blog