



{Governance} & Compliance
Translate policy into enforceable technical controls, automate compliance evidence collection, and close the gap between governance documents and runtime protection.
Operationalize Policy Into Technical Controls
Pillar translates governance policies into technical controls that enforce approved models, licensing standards, and data sovereignty requirements at every stage. Business context collected during discovery enables enforcement precision that distinguishes between a low-risk bot and a high-risk AI systems.

Approved Model Lists: Block deployment of unapproved models and frameworks.
Data Sovereignty Controls: Keep AI data in approved regions and meet residency requirements.
Licensing Compliance: Track model licenses and flag conflicts before they enter production.
RBAC for AI Assets: Control who can deploy models, access sensitive data, and modify policies.
Govern Third-Party AI and Supply Chain Risk
Pillar extends governance controls to external AI providers, SaaS platforms, and vendor integrations. The platform validates third-party AI systems against your security policies before they access internal data or production environments.
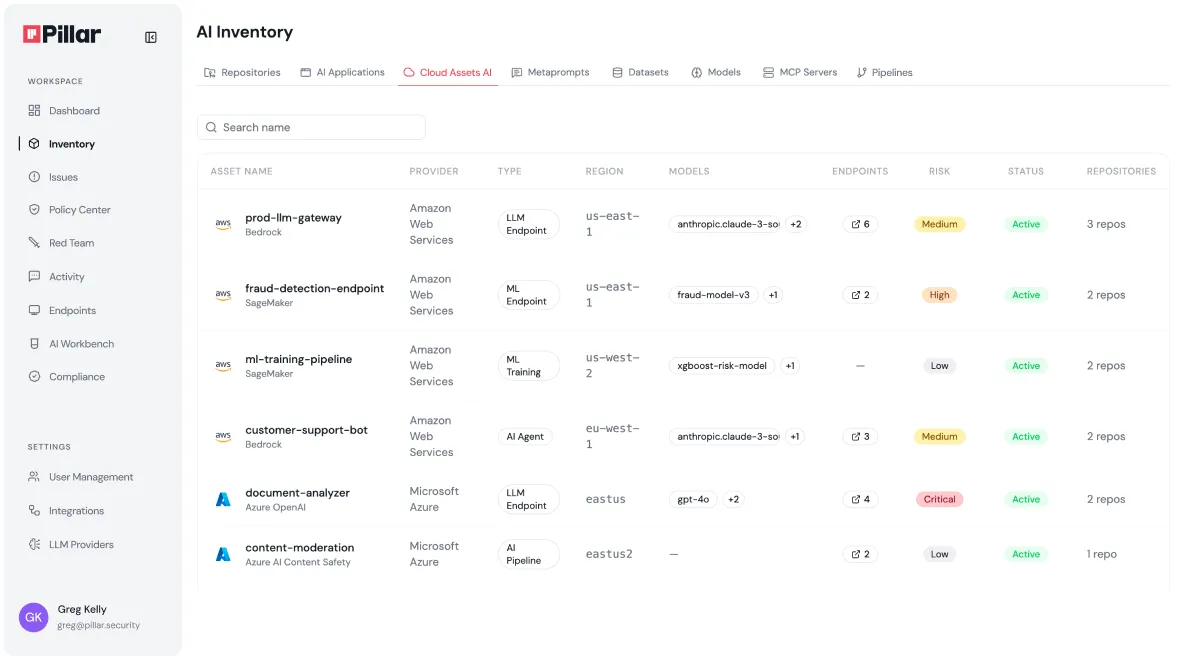
Third-Party AI Discovery: Identify external AI services, APIs, and integrations across your organization.
Vendor Risk Assessment: Evaluate AI providers against security and compliance requirements.
Policy Enforcement on External AI: Apply the same controls to vendor solutions as internal systems.
Supply Chain Validation: Track model provenance, licensing, and security posture for external AI components.
Automate Compliance and Framework Mapping
Pillar maps governance findings, testing results, and runtime logs to regulatory requirements automatically. The platform generates audit-ready documentation from discovery, red teaming, and guardrail telemetry without manual evidence collection.

Multi-Framework Mapping: Satisfy overlapping requirements across standards from a unified evidence base.
Automated Evidence Collection: Capture deployment approvals, risk assessments, and audit trails as systems operate.
Compliance Reporting: Generate documentation mapped to regulatory frameworks on demand for auditors.
Continuous Compliance Monitoring: Track policy coverage and governance gaps as your AI environment evolves.
“For the first time, our security team sees every model, dataset, and prompt in a single dashboard—no more chasing blind spots.”
"What impressed us most about Pillar was their holistic approach to Al security."
"We needed a security partner that not only pinpoints vulnerabilities but also helps remediate them automatically."
"By integrating Pillar’s advanced security guardrails, we ensure AI systems access only secure content, protecting our global customers."
See Pillar in action
What you'll see in 30 minutes
Discover every AI app, agent, MCP server, skill and coding assistant you build and run
Test your AI apps with agentic red teaming, with proof of every exploit
Protect AI apps, agentic endpoints and AI gateways from prompt injection and data leaks at runtime
Govern with one AI policy, mapped to OWASP, MITRE ATLAS, NIST and the EU AI Act
“What impressed us most about Pillar was their holistic approach to AI security.”
Raz Carmi, CISO


We've received your message, and we'll follow up via email shortly