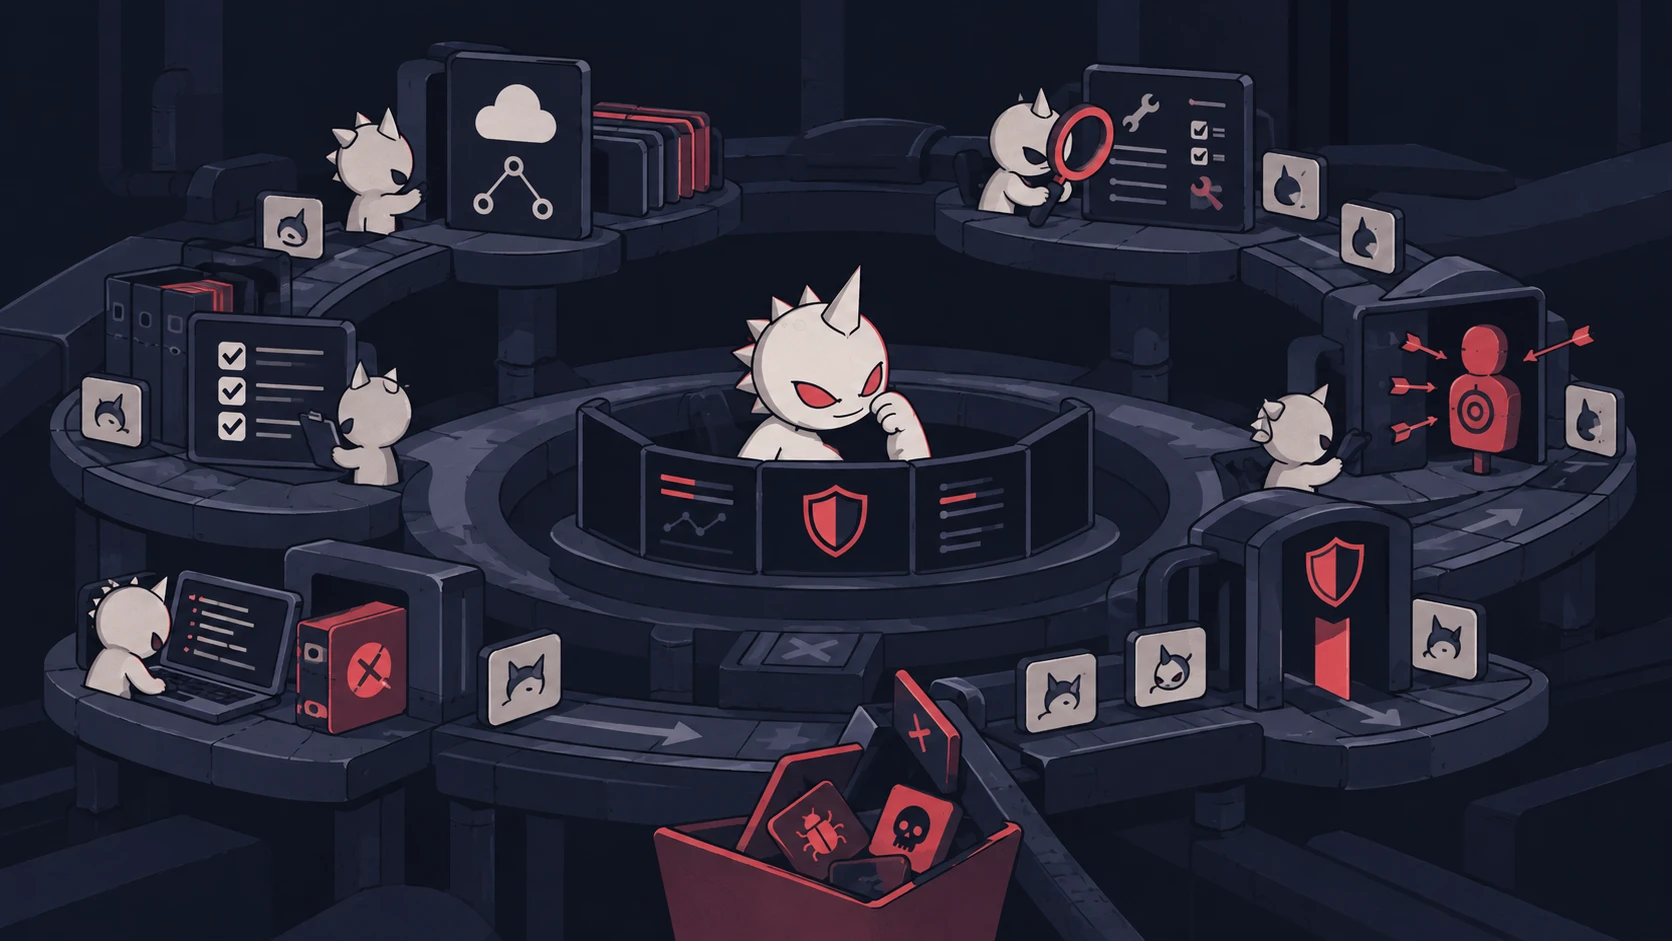






Model Context Protocol (MCP) lets AI agents call external tools through MCP servers, which often run with OAuth tokens, database credentials or cloud access. The main MCP security risks are poisoned tool descriptions, servers that accept unauthenticated calls, malicious or vulnerable server packages, indirect prompt injection through tool results, and over-broad permissions. The controls that reduce them start with an inventory of every MCP server in use, an allowlist of approved servers and tools, least-privilege credentials, and inspection of tool calls and results at runtime.
Updated October 11, 2026. First published March 24, 2025. This guide now covers the incidents and research published since then, including Pillar's own MCP disclosures, and the MCP specification released on July 28, 2026.
Key takeaways
- An MCP server acts with its own credentials, not the caller's. The two remote-server flaws Pillar disclosed in 2026 (Dolt MCP and Grafana MCP) both let an unauthenticated caller run tools with the server's credentials. Treat every MCP server as a privileged service.
- Tool descriptions are instructions to the model. A server can change what it tells the agent after it has been approved. Pillar found a live campaign in August 2026 whose server stayed harmless for its first three tool calls and then told the agent to collect SSH keys and cloud credentials.
- Approval is not a one-time event. Servers update, packages change hands and descriptions change at runtime. An allowlist needs version and behavior checks, not only names.
- Most enterprises don't know which MCP servers are running. Developers, and increasingly non-developers, add servers to Claude Code, Cursor, VS Code and Claude Desktop configurations without review. Inventory comes first.
- The protocol itself is tightening. The July 2026 specification adds stricter authorization checks and removes the session-ID mechanism that both Pillar disclosures abused. Servers built on older versions still need checking.
What is MCP, and how does it work?
MCP is an open protocol, released by Anthropic in November 2024 and now governed under the Linux Foundation, that standardizes how AI applications connect to tools and data. It has three parts:
- MCP clients and hosts: the AI applications that call tools, such as Claude Code, Cursor, VS Code, Claude Desktop and custom agents.
- MCP servers: programs that expose tools (actions), resources (data) and prompts to the client. A server can run locally on a developer's machine, communicating over standard input and output, or remotely over HTTP.
- The systems behind the server: email, files, databases, cloud APIs and SaaS applications, reached with credentials the server holds.
When a user asks an agent to do something, the model reads the list of tools and their descriptions, chooses a tool and sends a call. The server runs it with its own credentials and returns a result, which the model reads as input for its next step. Every part of that loop is a place an attacker can step in: the tool list, the description, the call, the server's authentication and the result.
MCP security best practices
Use this as a checklist. Each item maps to one or more of the risks below.
- Inventory every MCP server in use, on developer machines and in repositories, with the client it is configured in, its launch command or URL, its version and its source package.
- Approve servers against an allowlist, and block or flag any server that is not on it. Decide who can approve a server and how a request reaches them.
- Allow tools, not just servers. Approve the read tools a team needs and deny write or destructive tools (for example, allow issue search but deny delete) unless there is a reason.
- Pin versions and re-check every update. An approved server can ship a new version with new tools, new network destinations or new instructions.
- Give each server the least privilege it needs, with its own scoped credential. Don't reuse a personal token with full access across several servers.
- Keep secrets out of MCP configuration files. Use environment variables or a secret manager, and scan configuration files for hardcoded tokens.
- Require authentication on every remote server, and test that a rejected request is really rejected: the request must stop, not return an error and continue.
- Inspect tool descriptions, calls and results at runtime, not only the user's prompt. Instructions hidden in a tool description or a tool result are the main way an MCP server steers an agent.
- Turn off auto-approval for tool calls in agent settings, at least for write actions, and enforce it through managed settings that users can't change.
- Validate server-supplied URLs and hosts. A server that fetches a URL taken from the request can be turned against cloud metadata endpoints and internal services.
- Log every tool call with the user, agent, server, tool, arguments and result, and send it to your SIEM.
- Red-team agents through their tools, including a poisoned description, an injected tool result and an unapproved server, before release and after changes.
MCP security risks
| Risk | What happens | Control |
|---|---|---|
| Tool poisoning | Instructions hidden in a tool's description tell the model to do something the user didn't ask for, such as reading files or sending data out | Inspect tool descriptions when a server is added and at runtime; allow only reviewed servers |
| Rug pulls and runtime-gated metadata | A server behaves normally while it is reviewed, then changes its descriptions or behavior after an update or after a number of calls | Pin versions, re-scan updates, and inspect descriptions on every session, not just at install |
| Broken authentication on remote servers | A remote server checks a token or session ID only for its format, or returns an error but still runs the call, so an outside caller can use its tools | Test auth failure paths; adopt the 2026 specification's authorization requirements |
| Server credentials used for someone else's request | The server runs every call with its own service account, so whoever reaches the server gets that account's access | Scope each server's credential to its job; bind each call to an authenticated caller |
| Server-side request forgery (SSRF) | A server fetches a URL or host taken from the request, reaching cloud metadata endpoints or internal systems | Fix the target host in server configuration; block metadata endpoints |
| Malicious and vulnerable packages | A server package from a public registry contains malicious code, or a widely used MCP component has a remote-code-execution flaw | Install from vetted sources; check each package's publisher, version history and known vulnerabilities |
| Indirect prompt injection through tool results | Content a tool returns, such as an email, a web page or a database row, carries instructions the model then follows | Inspect tool results before the model reads them; require approval for sensitive follow-on actions |
| Over-broad permissions and token aggregation | One server, or one machine, holds tokens for many services with full scopes, so one compromise reaches all of them | Least-privilege scopes; separate credentials per server; short-lived tokens |
| Configuration tampering and auto-approval | An agent or an attacker edits an MCP configuration file to add a server or turn on auto-approval, and later calls run without review | Managed, read-only settings; alert on configuration changes; auto-approval off |
| Shadow MCP servers | Developers and non-developers add servers from wherever they find them, so security doesn't know they exist | Continuous discovery on endpoints and in repositories |
Real MCP incidents and vulnerabilities
| Date | Incident | Vector | Source |
|---|---|---|---|
| Aug 2026 | Deadbugz: an active campaign spread a malicious MCP server, "productivity-suite", through public GitHub pull requests. After three ordinary tool calls it changed its instructions, telling the agent to look for SSH keys, AWS credentials, shell history and Kubernetes configuration, and to hide this from the user. | Runtime-gated tool poisoning | Pillar Security |
| Aug 2026 | Dolt MCP authentication bypass (versions 0.3.1 to 0.3.6, fixed in 0.3.7): requests with invalid tokens got a 401 response but kept processing, and session validation accepted attacker-generated IDs. An unauthenticated caller could run database tools with the server's credentials. | Broken authentication | Pillar Security |
| Aug 2026 | Grafana MCP session spoofing and SSRF: the server accepted any well-formed caller-generated session ID, letting callers list and run tools with the server's Grafana service account (fixed in mcp-grafana 1.1.0). A second flaw let a caller-controlled header redirect requests, including to cloud metadata (CVE-2026-19516, CVSS 9.1). | Broken authentication; SSRF | Pillar Security |
| Sep 2026 | MCP Python SDK OAuth flaw: a malicious server could obtain a client's OAuth client secret. Fixed in SDK versions 1.30.0 and 2.2.0. | OAuth flow | GitHub advisory GHSA-qx49-fqc8-xw99 |
| Jul 2026 | AWS Kiro MCP configuration rewrite: the agent could be led to rewrite its own MCP configuration, leading to code execution. | Configuration tampering | CVE-2026-10591 |
| 2025 | postmark-mcp: the first malicious MCP server seen in the wild, published to a public package registry. | Malicious package | Cited in OWASP's State of Agentic AI Security and Governance |
| 2025 | mcp-remote command injection in a widely used MCP proxy component (CVE-2025-6514, CVSS 9.6). | Vulnerable component | CVE-2025-6514 |
| 2025 | GitHub MCP and Supabase MCP data exposure: proofs of concept in which content an agent read through an MCP tool led it to expose private data. | Indirect prompt injection | Cited as production examples under LLM01 in the OWASP Top 10 for LLM Applications 2026 |
The three Pillar disclosures share a pattern: the caller supplies the instruction, and the MCP server supplies the authority. Each server ran a request with its own credentials without confirming who had sent it.
How to enforce an MCP server allowlist
- Find the configurations. MCP servers are declared in each client's own settings files: Claude Code, Cursor, VS Code, Windsurf, Claude Desktop and others, at user, project and managed levels. Collect them from developer machines and from repositories, where project-level files are committed.
- Identify each server. Record the client, the launch command or remote URL, the package and version, and who installed it.
- Match each server against a vetted list. For each server, know what its tools can do (read, write, destructive), which network destinations it declares and which it actually contacts, who publishes it, and any known findings.
- Decide per server and per tool. Approve, approve with restrictions (for example, read tools only) or deny. Groups can have different lists; a data team and a platform team rarely need the same servers.
- Enforce where calls pass. For agents and applications that reach models through an AI gateway or an API, enforce the server and tool allowlist there. On developer machines, write the approved list into the client's managed settings through MDM so users can't override it, and block user-initiated installs where the client supports it.
- Re-check on every update. Treat a new version of an approved server as a new server until it has been checked, and alert when a server outside the list appears.
Where to enforce MCP security
There is no single control point, because MCP traffic takes different paths:
- At the AI gateway or API: covers agents and applications you build, where calls go through LiteLLM, Kong, TrueFoundry or another gateway. This is where a server and tool allowlist and tool-result inspection are easiest to apply centrally.
- On the developer machine: covers coding agents such as Claude Code, Codex CLI and Cursor, which start local MCP servers that never cross a gateway. Controls here are configuration posture (which servers are configured, whether auto-approval is on) and the agent's pre-tool hooks.
- In repositories and CI: covers MCP configuration committed to projects, which an agent picks up when someone opens the repository.
Most enterprises need all three. The AI gateway guardrails guide covers the gateway path, and the AI coding agent security comparison covers the endpoint.
How the MCP specification changed in 2026
The MCP specification released on July 28, 2026 added six authorization changes. Among them, clients must validate the authorization server's issuer, which closes OAuth mix-up attacks, and the Mcp-Session-Id mechanism was removed. The sampling and roots features are deprecated, with at least 12 months before removal. Governance of the protocol moved to the Linux Foundation. Servers built on earlier versions keep their old behavior until they are updated, so check which specification version each approved server implements.
How MCP risks map to OWASP and MITRE ATLAS
| Framework | Relevant entries |
|---|---|
| OWASP Top 10 for LLM Applications 2026 | LLM01 Prompt Injection (cites MCP proofs of concept), Excessive Agency, LLM06 (MCP amplification), LLM08 Hidden Context Exposure (now includes tool schemas) |
| OWASP Top 10 for Agentic Applications | ASI02 Tool Misuse, ASI04 Agentic Supply Chain (names MCP servers) |
| OWASP MCP Top 10 | MCP-specific risks, including MCP06 Intent Flow Subversion |
| OWASP Agentic Skills Top 10 | AST02 Supply Chain, AST07 Update Drift |
| MITRE ATLAS | AML.T0053 LLM Plugin Compromise; AI Agent Tool Poisoning, split in v2026.07 into definition and instructions, implementation, and runtime response |
The SAIL framework places these controls across the AI lifecycle, from inventory and posture to runtime.
How Pillar secures MCP
- Discovery: Pillar finds MCP servers configured on developer machines and in repository configuration files for Cursor, VS Code, Visual Studio, Windsurf, Codeium and Claude Desktop, and flags unapproved MCP clients.
- MCP intelligence: every server found is matched against Pillar's MCP catalog of more than 23,000 analyzed MCP servers, with a risk score, tool capabilities split into read and write or destructive, and declared and observed network destinations.
- Posture findings: findings such as MCP auto-approval enabled and channel-capable MCP servers show which configurations need fixing.
- Runtime enforcement: the MCP server allowlist and per-server tool permissions are one of Pillar's runtime guardrails, set in the Pillar console like any other guardrail, and enforced through LiteLLM and Pillar's API. Pillar also inspects tool descriptions, calls and results for poisoning and injection.
- Research: Pillar's researchers disclosed the Deadbugz campaign and the Dolt MCP and Grafana MCP vulnerabilities in 2026, and test agents' tools through red teaming.
Next steps
- Find the MCP servers your developers are running with Agentic Endpoint.
- Enforce MCP allowlists at your gateway with Runtime Guardrails.
- Read the research: Deadbugz, Dolt MCP and Grafana MCP.
FAQs
What are MCP security best practices?
Inventory every MCP server in use, approve servers and tools against an allowlist, pin and re-check versions, give each server a scoped credential, require and test authentication on remote servers, inspect tool descriptions, calls and results at runtime, turn off auto-approval, and log every tool call.
What is MCP tool poisoning?
Hiding instructions in an MCP tool's description so the model follows them. The model reads tool descriptions as guidance, so a poisoned description can make an agent read files or send data without the user asking.
What is an MCP rug pull?
A server that behaves well when it is reviewed and approved, then changes its tools, descriptions or behavior later, through an update or after a number of calls. Pillar's Deadbugz disclosure described a server that changed its instructions after three tool calls.
How do I enforce an MCP server allowlist on developer machines?
Write the approved servers into each client's managed settings through MDM, block user-initiated installs where the client allows it, scan endpoints and repositories for servers outside the list, and re-check approved servers when they update.
Are local MCP servers safer than remote ones?
Local servers aren't exposed to the internet, but they run with the developer's own access and are installed with little review. Remote servers must handle authentication correctly, and the 2026 disclosures show that some don't. Both need inventory and an allowlist.
Why are MCP servers a high-value target?
They hold credentials, often for several services, and run actions with them. Whoever can make a server act, whether through a poisoned description, an injected result or a broken authentication check, gets that server's access.
Does the 2026 MCP specification fix these problems?
It tightens authorization and removes the session-ID mechanism abused in the Dolt and Grafana cases, but it doesn't stop tool poisoning, malicious packages or prompt injection through tool results, and older servers keep their old behavior until updated.
Can an AI gateway secure MCP?
For traffic that passes through it, yes: a gateway can enforce a server and tool allowlist and inspect tool calls and results. Local MCP servers started by coding agents on developer machines don't pass through a gateway, so they need endpoint controls as well.
Subscribe and get the latest security updates

Back to blog